Microsoft исправляет ошибку безопасной загрузки, позволяющую установить руткит Windows
Microsoft исправила уязвимость обхода функции безопасности в Secure Boot, которая позволяет злоумышленникам нарушить процесс загрузки операционной системы, даже если безопасная загрузка включена.
Безопасная загрузка блокирует ненадежные загрузчики операционных систем на компьютерах с микропрограммой Unified Extensible Firmware Interface (UEFI) и микросхемой доверенного платформенного модуля (TPM), чтобы предотвратить загрузку руткитов во время процесса запуска ОС.

Руткиты могут использоваться злоумышленниками для внедрения вредоносного кода в прошивку UEFI компьютера, для замены загрузчика операционной системы, для замены частей ядра Windows или маскировки вредоносных драйверов, являющихся законными драйверами Windows.
Уязвимость обхода функции безопасности, отслеживаемая как CVE-2020-0689 , имеет общедоступный код эксплойта, который работает во время большинства попыток эксплуатации, требующих запуска специально созданного приложения.
«Злоумышленник, успешно воспользовавшийся уязвимостью, может обойти безопасную загрузку и загрузить ненадежное программное обеспечение», — объясняет Microsoft.
Затронутые версии Windows включают несколько выпусков Windows 10 (от v1607 до v1909), Windows 8.1, Windows Server 2012 R2 и Windows Server 2012.
Обновление безопасности KB4535680 исправляет уязвимость безопасной загрузки UEFI
Устройства Windows, имеющие встроенное ПО на базе UEFI, могут работать с включенной функцией безопасной загрузки (Secure Boot). База данных запрещенных подписей безопасной загрузки (DBX) предотвращает загрузку уязвимых модулей UEFI.
В защищенной загрузке существует уязвимость обхода функции безопасности (CVE-2020-0689). Злоумышленник, успешно воспользовавшийся этой уязвимостью, может обойти безопасную загрузку и запустить недоверенное ПО на целевом компьютере.
Обновление KB4535680 добавляет сигнатуры известных уязвимых UEFI модулей в DBX.
Установка через Центр обновления Windows
Обновление 4598229 для ПК устанавливается автоматически через Центр обновления Windows для поддерживаемых систем. Для проверки перейдите в меню Параметры > Обновление и безопасность и нажмите Проверить наличие обновлений.

Для завершения установки потребуется перезагрузка компьютера.
Скачать обновление KB4535680
Вы также можете скачать обновление из Каталога Центра обновления Майкрософт и установить его вручную по ссылке ниже:
Обновление безопасности KB4535680 исправляет уязвимость безопасной загрузки UEFI
Обновление безопасности KB4535680 вносит улучшения в список Secure Boot DBX для следующих поддерживаемых версий Windows:
- Windows Server 2012 x64-bit
- Windows Server 2012 R2 x64-bit
- Windows Server 2016 x64-bit
Устройства Windows, имеющие встроенное ПО на базе UEFI, могут работать с включенной функцией безопасной загрузки (Secure Boot). База данных запрещенных подписей безопасной загрузки (DBX) предотвращает загрузку уязвимых модулей UEFI.
В защищенной загрузке существует уязвимость обхода функции безопасности (CVE-2020-0689). Злоумышленник, успешно воспользовавшийся этой уязвимостью, может обойти безопасную загрузку и запустить недоверенное ПО на целевом компьютере.
Обновление KB4535680 добавляет сигнатуры известных уязвимых UEFI модулей в DBX.
Установка через Центр обновления Windows
Обновление 4598229 для ПК устанавливается автоматически через Центр обновления Windows для поддерживаемых систем. Для проверки перейдите в меню Параметры> Обновление и безопасность и нажмите Проверить наличие обновлений.
Для завершения установки потребуется перезагрузка компьютера.
Скачать обновление KB4535680
Вы также можете скачать обновление из Каталога Центра обновления Майкрософт и установить его вручную по ссылке ниже:
KB4535680 for Windows 10 to Fix UEFI Secure Boot Vulnerability
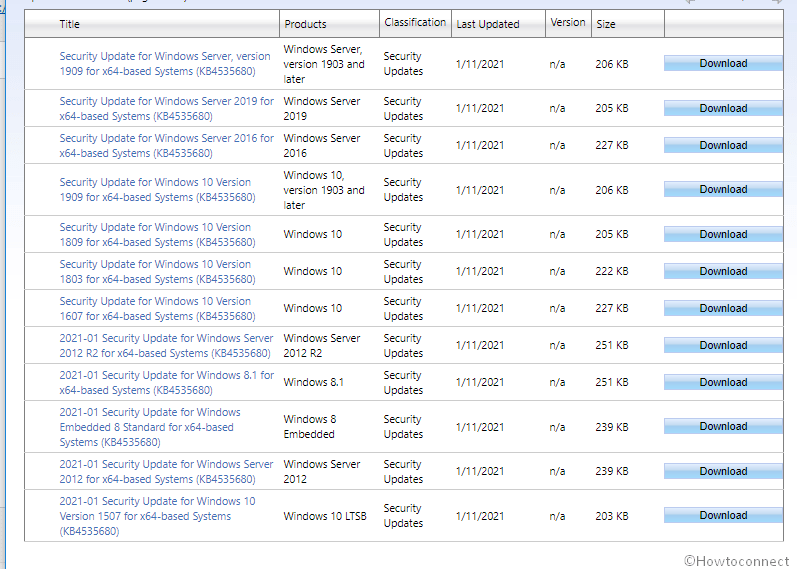
On patch Tuesday, Microsoft is rolling out an update to fix an issue in Secure boot vulnerability CVE-2020-0689. KB4535680 is the Security patch that adds the signatures of the known vulnerable UEFI modules to the DBX to address the vulnerability.
You can receive the patch as usual through the automatic update moreover from Microsoft update catalog. The devices will not need to be restarted to complete the installation.
KB4535680 for Windows 10 will Fix UEFI Secure Boot Vulnerability
The update will support the following versions –
- Windows 10 v1909 x64-bit
- Windows 10 v1809 x64-bit
- Windows 10 v1803 x64-bit
- Windows 10 v1607 x64-bit
- Windows Server 2019 x64-bit
- Windows Server 2016 x64-bit
- Windows 8.1 x64-bit
- Windows Server 2012 R2 x64-bit
- Windows Server 2012 x64-bit
Security patch improves the Secure Boot DBX for the supported Windows versions.
Key changes
Windows devices that have UEFI based firmware are able to run with Secure Boot enabled. The Secure Boot Forbidden Signature Database (DBX) prevents UEFI modules from loading. This update adds modules to the DBX.
A vulnerability that has the capability of bypassing security features lives in the secure boot. An intruder who successfully exploited the vulnerability might bypass secure boot and load untrusted software.
This security patch addresses the vulnerability by adding the signatures of the known vulnerable UEFI modules to the DBX.
Known Issues
| Issue | Workaround |
| Some original equipment manufacturer (OEM) firmware might not allow for the installation of this update. | To resolve this issue, contact your firmware OEM. |
| If BitLocker Group Policy Configure TPM platform validation profile for native UEFI firmware configurations is enabled and PCR7 is selected by policy, it may result in the BitLocker recovery key being required on some devices where PCR7 binding is not possible. |
To view the PCR7 binding status, run the Microsoft System Information (Msinfo32.exe) tool with administrative permissions.
Important Changing from the default platform validation profile affects the security and manageability of your device. BitLocker’s sensitivity to platform modifications (malicious or authorized) is increased or decreased, depending on inclusion or exclusion (respectively) of the PCRs. Specifically, setting this policy with PCR7 omitted, will override the Allow Secure Boot for integrity validation Group Policy. This prevents BitLocker from using Secure Boot for platform or Boot Configuration Data (BCD) integrity validation. Setting this policy may result in BitLocker recovery when the firmware is updated. If you set this policy to include PCR0, you must suspend BitLocker before you apply firmware updates.
· On a device that does not have Credential Gard enabled, run following command from an Administrator command prompt to suspend BitLocker for 1 reboot cycle:
Manage-bde –Protectors –Disable C: -RebootCount 1
Then, restart the device to resume the BitLocker protection.
Note Do not enable BitLocker protection without additionally restarting the device as it would result in BitLocker recovery.
· On a device that has Credential Guard enabled, there may be multiple restarts during the update that require BitLocker to be suspended. Run the following command from an Administrator command prompt to suspend BitLocker for 3 restart cycles.
Manage-bde –Protectors –Disable C: -RebootCount 3
This update is expected to restart the system two times. Restart the device once again to resume the BitLocker protection.